Trusted by Leading Security Teams
You can't hire your way out of this.
Your team runs dozens of tools and still can't prove there are no blind spots. More than 80% of last year's breaches were preventable with controls you already owned, the data was there. Nobody connected it in time.
The context isn't in one place and it isn't only logs
An EDR can block a malicious process and never tell your email gateway that two other people got the same message.
Static rules and alert queues were built for a slower world
A static rule only catches what someone already wrote a rule for, and an alert queue only moves as fast as the analyst working it.
The SIEM was built for humans to query, not for AI to reason
A SIEM waits for you to write the query and read the result. It can't choose which sources to pull, correlate them, and reach a verdict on its own.
100x your security engineers
Scale your best analysts' judgment across every alert, hunt, and response workflow. Don't burn them on pivoting between consoles and rewriting the same queries by hand. Let them hunt, harden detections, and make the calls that actually need a human.
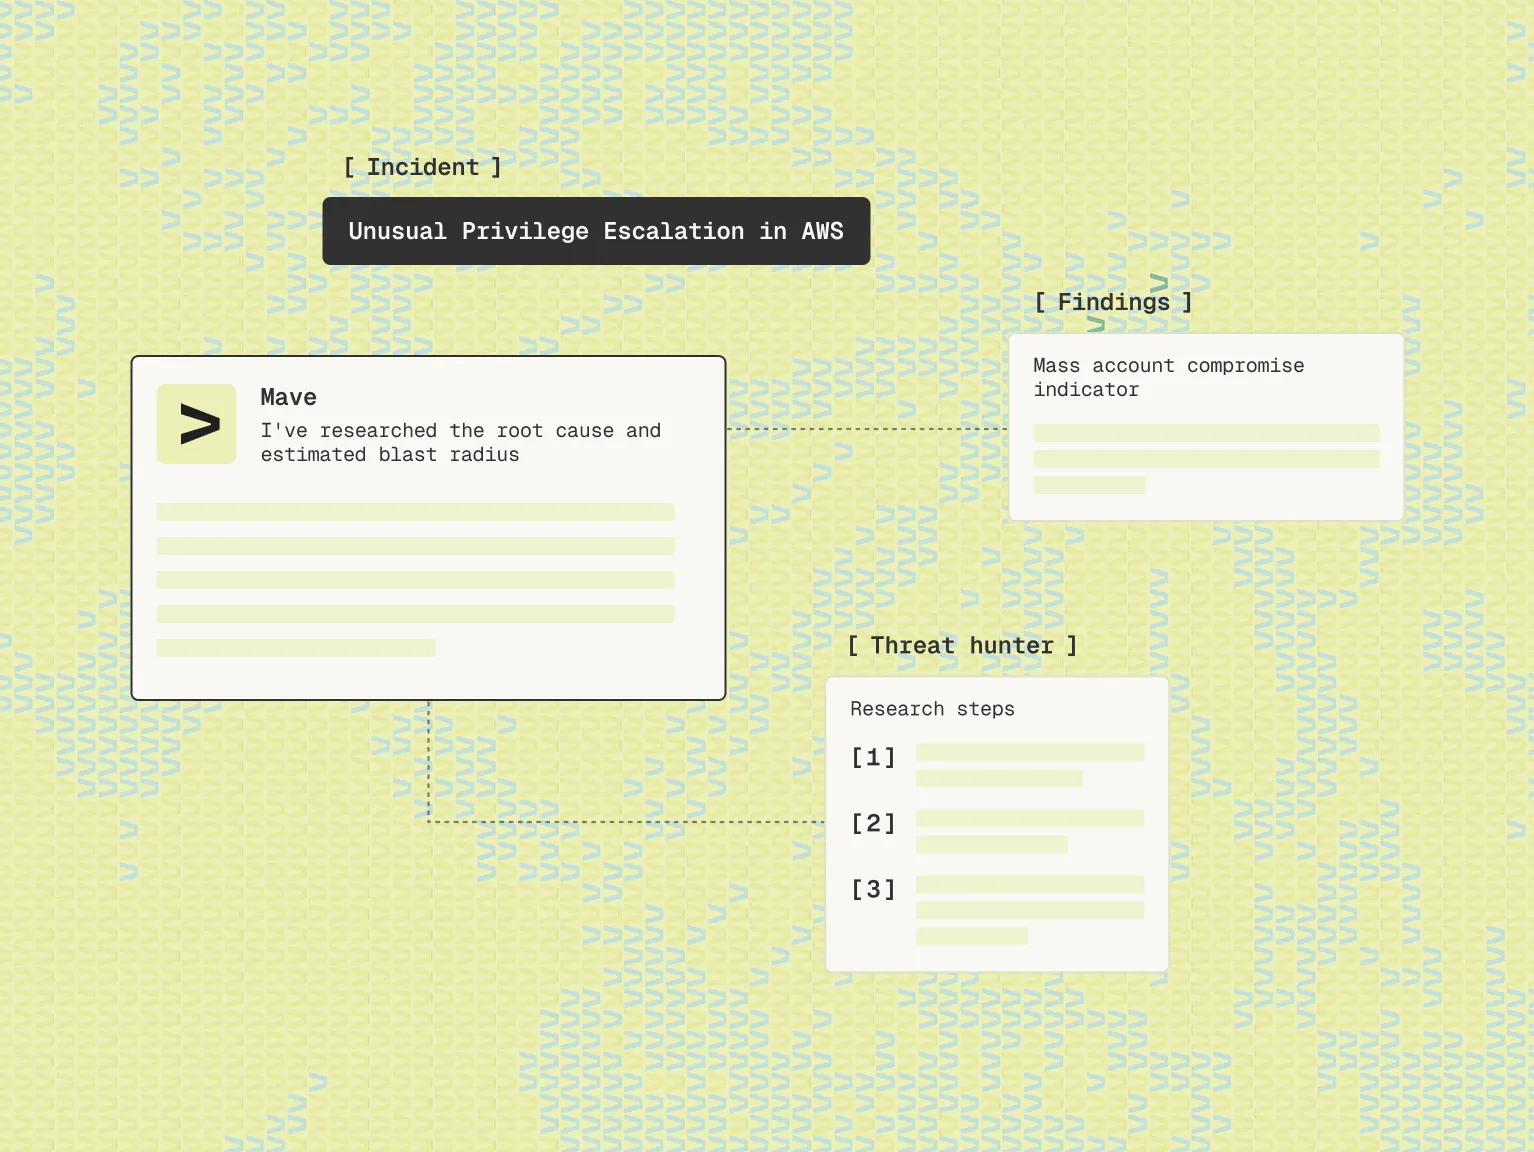
Cover what your team can't
Mave scores live campaigns against your actual environment, watches for dormant indicators reactivating, and hunts continuously between incidents - so the search for what never alerted isn't gated on someone having a free afternoon
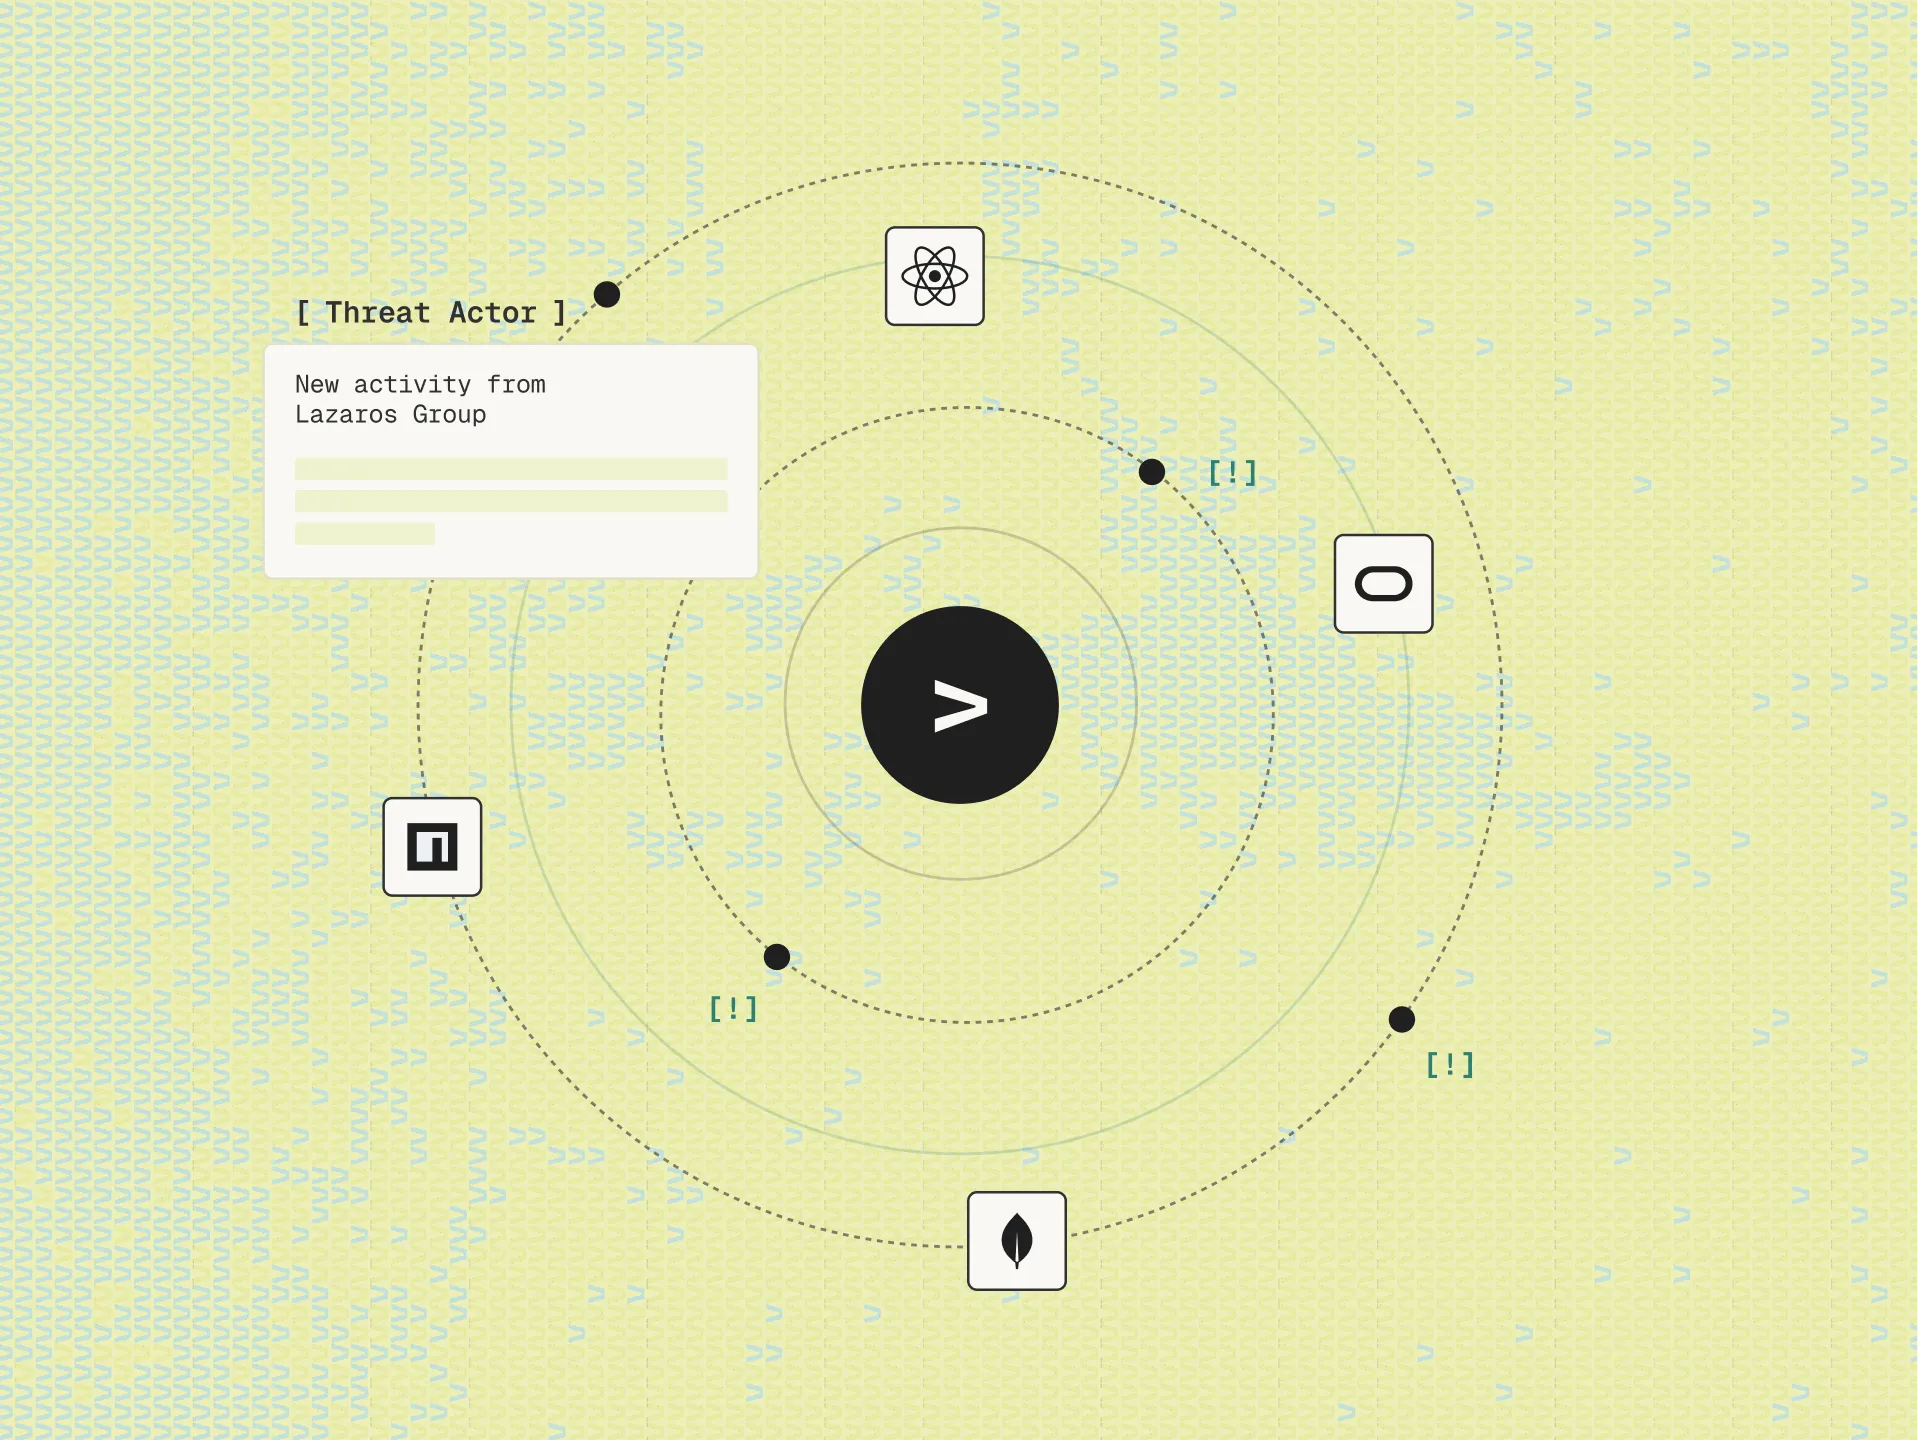
Respond under your rules
You set what runs automatically and what waits for a human: notify, ticket, document, or remediate. Destructive actions stay behind approval by default, every step is scoped by least-privileged permissions, and the full action trail is logged
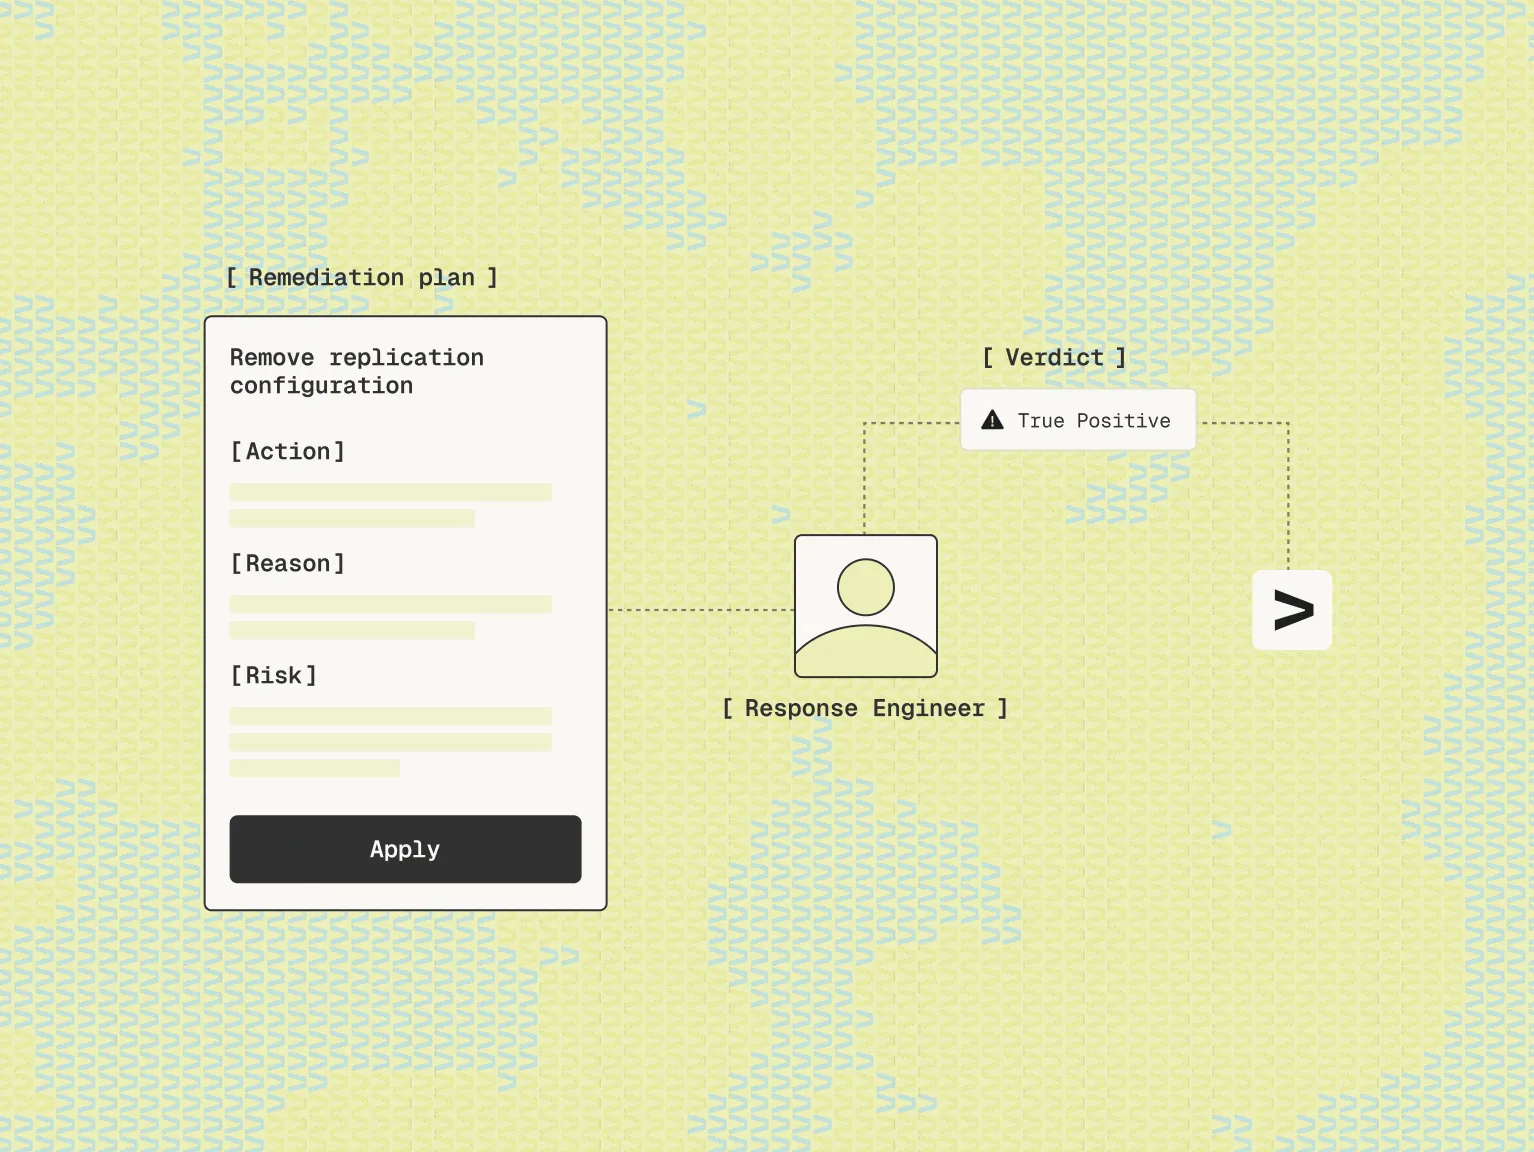
No ingestion. No manual queries.
Live context layer.
Prepare for the threats that haven't reached you yet
Mave projects live threat campaigns onto your actual environment, hunts continuously across your telemetry, and hardens your detections against the gaps and noise that static rules leave behind

Investigate every alert, and answer any question
Mave pulls alerts, gathers context from every connected tool, and returns an evidence-backed verdict. Ask Mave lets your team query the entire stack in plain language, no query syntax required

Turn any finding into governed action
Every verdict, IOC, or agent finding can trigger a response, generated from the live investigation rather than a playbook written last year. You are fully in control of exactly what runs automatically.

What Security Leaders Say
As an MSSP, we work across different client security stacks. Mave was the first agentic platform that held up across them. Its agents investigate alerts in place, using tools clients already own, without re-ingestion. Analysts open cases with correlation, telemetry verification, and reasoning already done, so they focus on judgment instead of tab-switching. Every investigation is fully auditable, so when clients ask why something was closed, we can show exactly what was queried and why. Ask Mave also lets analysts, engineers, and Customer Success pull answers directly from their data.
Mave provides a single, centralized platform for managing investigations across most of our relevant systems. It has dramatically reduced investigation time for our analysts, helped us quickly identify visibility gaps, and enabled us to make faster, data-driven decisions based on up-to-date information. The platform delivers significant value that would have taken us a long time to build internally, while also providing very fast time-to-value and a smooth onboarding experience. In addition, it helps other teams within the CIO organization work more efficiently and securely, with real-time, security-focused, reliable data and minimal operational effort.
In a high-stakes stock exchange environment, zero latency and total visibility are non-negotiable. Mave Security transformed our SOC operations by consolidating our threat monitoring into a single, AI-driven platform. It automatically correlates complex telemetry, slashes alert fatigue, and drastically lowers our response times. Mave gives us the continuous, audit-ready protection essential for safeguarding critical financial infrastructure.
Mave has overcome the data silos barrier. My team can threat hunt across all platforms in seconds, and I no longer need to chase broken pipelines or schema drifts.
Within a few days the AI agents were already running on their own and producing findings the team could act on. I run an ERP company, not a 50-person SOC. The fact that my people picked Mave up and started getting value out of it without a training program is what made this a real product for us, not a science project.
Integrating Mave is less like deploying another security product and more like bringing on a team of expert security engineers and analysts who already know how to operate every tool in your stack. It really is the Swiss Army knife of SecOps. Any action an analyst can take across your environment, Mave can take autonomously, faster and far more consistently.
Agentic execution, governed by your rules

Approval gates
Require review for workflow actions and detection updates, automate only what you’re comfortable with.

Least-privileged architecture
Fine-grained, per-platform API permissions. Read-only on day one.

Complete audit trail
See exactly what every agent queried, how it correlated, what it concluded, and why.

Bring your own context
Enrich your Mave environment with your knowledge base—policies, naming, ownership, and exceptions—so it works the way your environment actually runs.